Author Posts
Armatyr Team
Posts by Armatyr Team
Read More
Armatyr is live — a new medical device cybersecurity consultancy built to help manufacturers secure their devices by design, backed by over a decade of combined academic and industry experience....
Read More
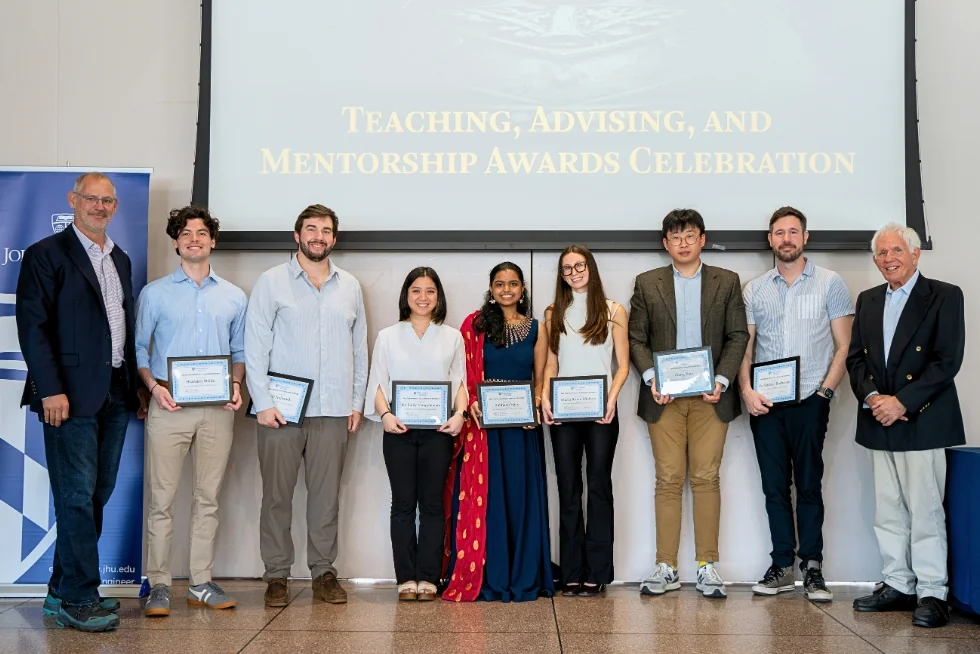
Armatyr co-founder Dr. Michael Rushanan has received the 2026 Joel Dean Excellence in Teaching Award from the Johns Hopkins Department of Computer Science.
Kaixin Du, Dibyajyoti Nath, Ramit Saraswat, Zhicheng Sun, Michael Rushanan, and Tushar M. Jois. "A Hands-On Platform for Medical Device Security Education." ACM SIGCSE Technical Symposium, 2026.
Armatyr co-founder Dr. Michael Rushanan is directing the Health and Medical Security (HMS) Lab at Johns Hopkins University, continuing its work on security vulnerabilities affecting health systems and medical devices....
Michael Rushanan. "If They Can Touch It, They Own It: The Stories We Tell Ourselves About Medical Device Cybersecurity." Proceedings of USENIX Security Symposium Enigma Track, 2026.
The authors propose a zero-knowledge approach that lets a medical device manufacturer prove an SBOM meets a regulator's requirements without disclosing the underlying component details. Building on their own prior...
The authors study the tension between publishing SBOMs for transparency and the risk that the same documents give attackers a ready-made map of a healthcare system's exploitable software components. Using...
The authors examine the gap between an SBOM that satisfies FDA premarket cybersecurity guidance on paper and one that is actually complete enough to support real vulnerability response. Using an...
Dr. Michael Rushanan presented "Building Medical Devices With Security by Design" at DC Systems 007.
The Johns Hopkins Hub featured Dr. Michael Rushanan's Medical Device Cybersecurity class.
Dr. Michael Rushanan joined The Health Beat podcast to talk about where security and medicine intersect.
Dr. Michael Rushanan presented "DIY Diabetics and a Million Boluses" at the DEF CON 28 Biohacking Village.
Dr. Michael Rushanan presented a UL Solutions webinar on the security challenges of interoperable smart infusion pumps.
Dr. Michael Rushanan presented "The Attack Surface of a Networked Medical Device" at the DEF CON 27 Biohacking Village.
Dr. Michael Rushanan spoke with ABC Radio National's Health Report about pacemaker security.
The authors explore how secure location-sensing systems can be applied in hospital settings to track equipment and staff while protecting against spoofing and unauthorized tracking. They introduce Beacon+, a Bluetooth...
The authors show how HTML5 Web Workers can be abused to perform stealthy computation and establish covert communication channels inside a victim's browser, without the user's knowledge. Because Web Workers...
The authors introduce a wearable bracelet that uses the Kerberos protocol to give hospital staff fast, secure authentication to shared workstations without repeatedly re-entering credentials. After a single login, the...
In this video, the authors evaluate the use of a patient's own heartbeat (ECG) as a cryptographic key source for securing communication between implantable medical devices.
The authors systematize a decade of research on the security and privacy of implantable medical devices and body area networks, mapping the field's threat models, proposed defenses, and open problems....
The authors present an encryption framework designed to protect medical images without the performance overhead that makes standard encryption impractical for large-scale imaging systems.